Programs often read configuration files at startup, even when those files never change after the program is built. With C++26, you can eliminate that entire step by having the compiler read, parse, and validate the configuration at compile time, leaving only the finished data in the executable…
Flock Safety, the embattled vendor of mass surveillance technology, has rolled out a handful of new reforms intended to appease the justified nationwide anger that has seen scores of towns cancel or suspend their contracts with the company for automated license plate readers (ALPRs). The reforms…
The Securities and Exchange Commission today charged three Toms River, New Jersey residents for their roles in an affinity investment fraud that raised approximately $47 million from more than 87 investors, who were primarily members of Orthodox Jewish…
TL;DR: LLM predictions can stand in for human outcomes in A/B tests, but only by assumption, not by design.... The post When Can LLMs Replace Humans in A/B Tests? appeared first on Spotify Engineering.
Packer v1.16.0 adds native SLSA provenance generation and verification for machine images, along with new HCL2 features for provisioners and variables.
Members Newsletter – August 2026: Every model making headlines today, open or closed, sits on top of Open Source code, runs on Open Source infrastructure, and is based on openly shared research. That's not sentiment, it's just the history of how we got here. None of this exists without the Open…
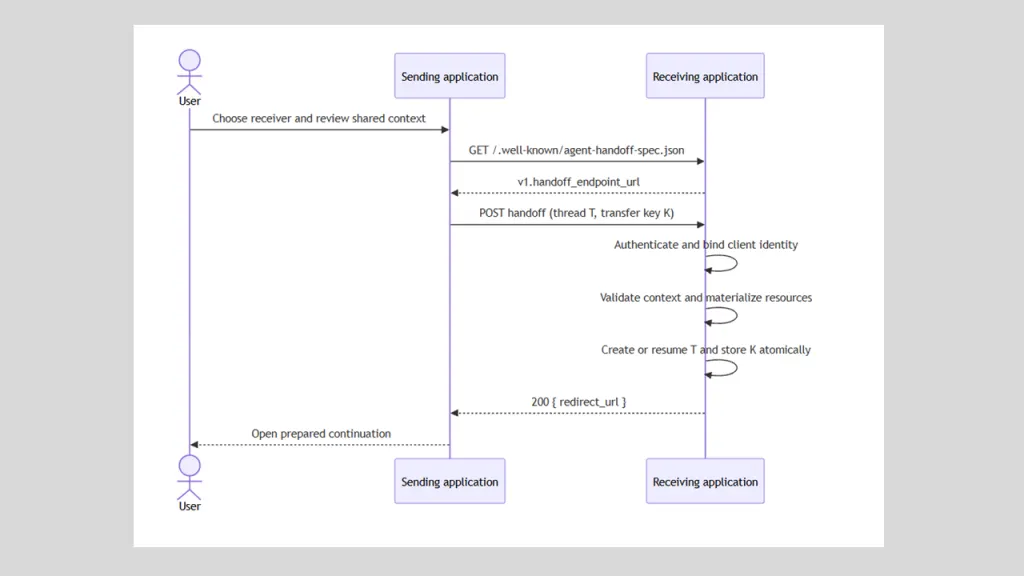
DeepJudge, the Zurich-based enterprise search company that describes itself as the institutional intelligence platform for legal AI, today introduced the Agent Handoff Protocol, an open protocol designed to let users move from one AI product into another – and, in some cases, back again – while…
A Shopify fake refund scam has been making the rounds over the past few months, targeting Shopify’s Shop app users directly within the app. Here’s what to know.
ClickStack and Hud now share trace IDs, pairing service-level observability with function-level runtime forensics so coding agents can assess risky changes before they ship, catch regressions right after deploy, and fix them with real production context.
Over the last month, the EU has passed two milestones in implementing its Cyber Resilience (CRA) and AI acts. The OSI has been engaged with European policymakers over the past two years to ensure those laws don’t inadvertently harm Open Source.
I just released Neon for Herdr, a Herdr plugin that puts your Neon projects in a pane next to whatever you are already doing, so creating a branch, grabbing its connection string, or suspending a compute is only a keypress away.
We are advancing a connected set of efforts to strengthen online safety and security for people and communities worldwide. The post Advancing the Safer Internet Initiative for Everyone appeared first on Internet Society.
Preview Ultrafast, a new OpenAI API service tier that runs GPT-5.6 Sol up to 14× faster. Powered by Cerebras, it delivers up to 750 output tokens per second.
This vulnerability allows remote attackers to execute arbitrary code on affected installations of NVIDIA Transformers4Rec. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8…
This vulnerability allows remote attackers to execute arbitrary code on affected installations of BlackBerry QNX. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The…
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute high-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5.
This vulnerability allows remote attackers to create a denial-of-service condition on affected installations of dnsmasq. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5. The following CVEs are assigned: CVE-2026-4890.
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Cisco Identity Services Engine. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2026-20147.
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute high-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5.
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute high-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5.
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute high-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5.
This vulnerability allows local attackers to escalate privileges on affected installations of Gen Digital CCleaner. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The…
This vulnerability allows local attackers to escalate privileges on affected installations of Norton Utilities Ultimate. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8…
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Cisco Identity Services Engine. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 4.9. The following CVEs are assigned: CVE-2026-20148.
This vulnerability allows local attackers to escalate privileges on affected installations of Trend Micro VPN. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.0. The…
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute high-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5.
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Cisco Identity Services Engine. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2026-20181.
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute high-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5.
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following…
This vulnerability allows remote attackers to execute arbitrary code on affected installations of NGINX. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.1. The following CVEs are assigned: CVE-2026-27654.
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute high-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5. The following…
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Clam AntiVirus. Interaction with this product is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 8.4. The…
The vulnerability allows remote attackers to disclose sensitive information on affected installations of Cisco Identity Services Engine. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5. The following CVEs are assigned: CVE-2026-20190.
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Linux Kernel KSMBD. Authentication is not required to exploit this vulnerability. However, only systems with ksmbd enabled are vulnerable. The ZDI has assigned a CVSS rating of 9.3. The…
The best way to learn is by shipping product to users in production, and that's why we don’t treat our interns as temporary guests. Every intern at Vercel is expected to operate like a core part of our engineering team from day one. This past winter, we welcomed a small cohort of those interns to…
New understanding of how nuclear fuel breaks down and changes in an operating nuclear reactor could help keep some reactors running longer, will inform the next generation of nuclear reactor fuel systems.
Some deals expected to be up for renewal are banking giant HSBC’s ERP implementation and modernisation contract with Accenture and Capgemini, Wipro’s contract with ICICI Bank, Tata Consultancy Services’ engagements with GE Healthcare, TCS and HCLTech’s contracts with Cemex, among others, said…
Staffing firms told ET that more than a third of experienced professionals hired by the 150 largest GCCs in India in the past year came from IT services companies. The remaining two-thirds were a mix of talent from GCCs, product companies, startups, consultancies and other sectors, they said.
AI SDK harness layer HarnessAgent @ai-sdk/harness-acp Thenow supports any Agent Client Protocol (ACP)-compatible harness withthrough the newpackage. @ai-sdk/harness-acp Previously, every harness adapter wrapped one specific runtime (Claude Code, Codex, Pi, Deep Agents, OpenCode).wraps the protocol…
AI SDK harness layer HarnessAgent Thelets you run established coding-agent runtimes through one unified interface, so you can switch runtimes without changing your application code. Today we are adding Grok Build, which runs through the sameinterface as every other supported harness…
Gemini 3.7 Flash AI Gateway from Google is now available onfor 50% off till December 31st, 2026. Gemini 3.7 Flash improves on prior Flash models at software engineering and agentic work. It resolves issues more reliably and spends less time stuck in failed agent loops, which matters on long…
GLM 5.2 eve Blackbox AI AI Gateway , the open-weights coding model from Z.ai with a 1M-token context window, is free foragents through August 27, served byon. npx eve@latest init my-agent New eve agents come with GLM 5.2 as their default model. Useto get started. agent/agent.ts Existing agents can…
Team owners and members can now upgrade all projects using Node.js 20 or earlier to Node.js 24 with one click from the Vercel Dashboard. Node.js version in project settings package.json This updates the. If your project also defines a version in, you'll need to update it manually. Existing…