Vercel Connect now gives teams line-level visibility into the token lifecycle. See who created a token, what app or project used it, when, and whether it is still active. Observability Every connector's detail page includes a newtab: Connect observability is available on all plans. Events are…
Every build on Vercel starts in the build warm pool, which is a set of standby containers that let builds begin without waiting for new compute. The pool runs on state that tracks which containers are ready, the tokens each one uses to authenticate, and the mapping that ties every running build…
Microsoft today released updates to remedy at least 398 security vulnerabilities in its Windows operating systems and supported software, including one weakness that is already being actively exploited and two others that were publicly detailed prior to today.
CSET’s Steph Batalis shared her expert insight in an article published by The Washington Post. The article examines how AI-generated viruses could support new approaches to vaccine development and treatments for antibiotic-resistant bacteria, while raising concerns about the potential misuse of AI…
The two papers we are covering today are complementary in a philosophical sense. They both improve how string literals are handled in C++26. P2361R6 tackles strings that are never evaluated — the ones that only exist at compile time. P1854R4 tackles evaluated string literals, making non-encodable…
Enterprise Managed Users (EMU) gives organizations full control over the Vercel accounts tied to their verified domains. It makes the organization's identity provider the single source of truth for authentication and account lifecycle, so accounts on company domains are governed centrally rather…
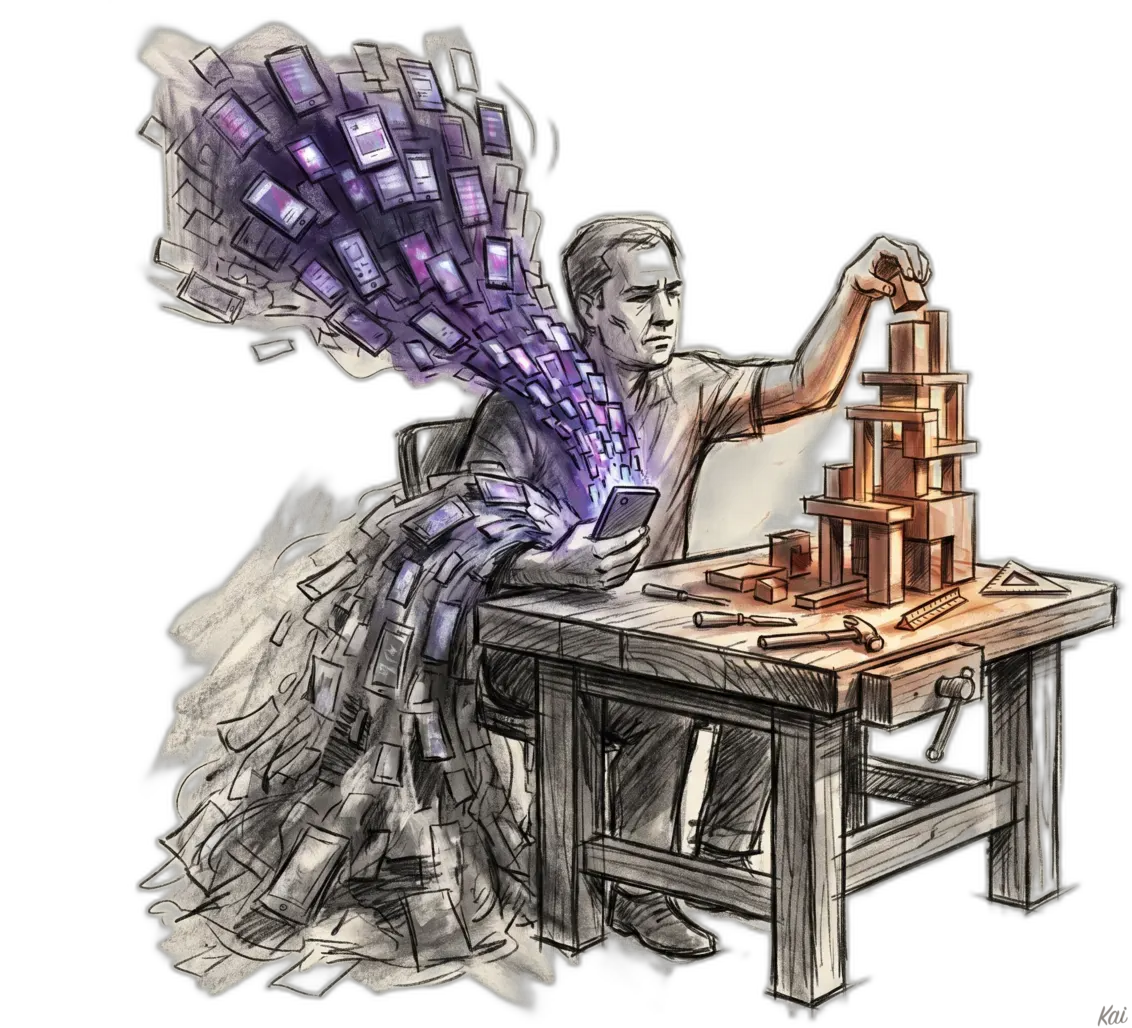
Charcoal sketch of a seated figure whose left arm dissolves into a cascade of purple glowing phones while their right hand builds a warm wooden tower/images/creativity-vs-consumption-header.webp/images/creativity-vs-consumption-header.webp If there's one metric to watch for managing your…
Snipe-IT Checkout Request Cancellation IDOR Snipe-IT is an open-source IT asset management application developed by Grokability, Inc. The endpoint that cancels asset checkout requests, POST /account/request/{itemType}/{itemId}/{cancel_by_admin?}/{requestingUser?}, trusts two user-controlled URL…
We’ve had a few questions from EFF supporters lately, asking whether the images we use on our blog posts, or on donation and shop items, have been created with AI image generators. We’d like to answer these questions and clarify our internal policy regarding image creation. EFF images are all made…
Video is a core data path across NVIDIA Jetson applications, from robotics and intelligent video analytics to industrial automation, healthcare, media...
vercel connect create You can now integrate 100+ services through Vercel Connect from the CLI. Previously,completed setup in the terminal for some services, and opened the dashboard for everything else. Pass the service name to create a connector, then attach it to your project: The CLI…
YAML has been the standard way to write Kubernetes manifests for years. Every example, tutorial, and configuration file you come across is written in it. The problem isn't that YAML is a bad format. It's that YAML gives you a lot of choices, and not all of them are equally good for writing…
For ambitious software startups, winning a new customer is only the beginning. The next challenge is getting that customer fully operational before delays, technical complications, or a difficult data migration undermine the relationship. Universal Migrator helps fast-moving startups accelerate…
Ryan Greenblatt is the Chief Scientist at Redwood Research, where he works on technical AI safety research. He's also lead author on the "Alignment faking in Large Language Models", and is currently working on a third party investigation into the OpenAI/HuggingFace incident. In my opinion, he's one…
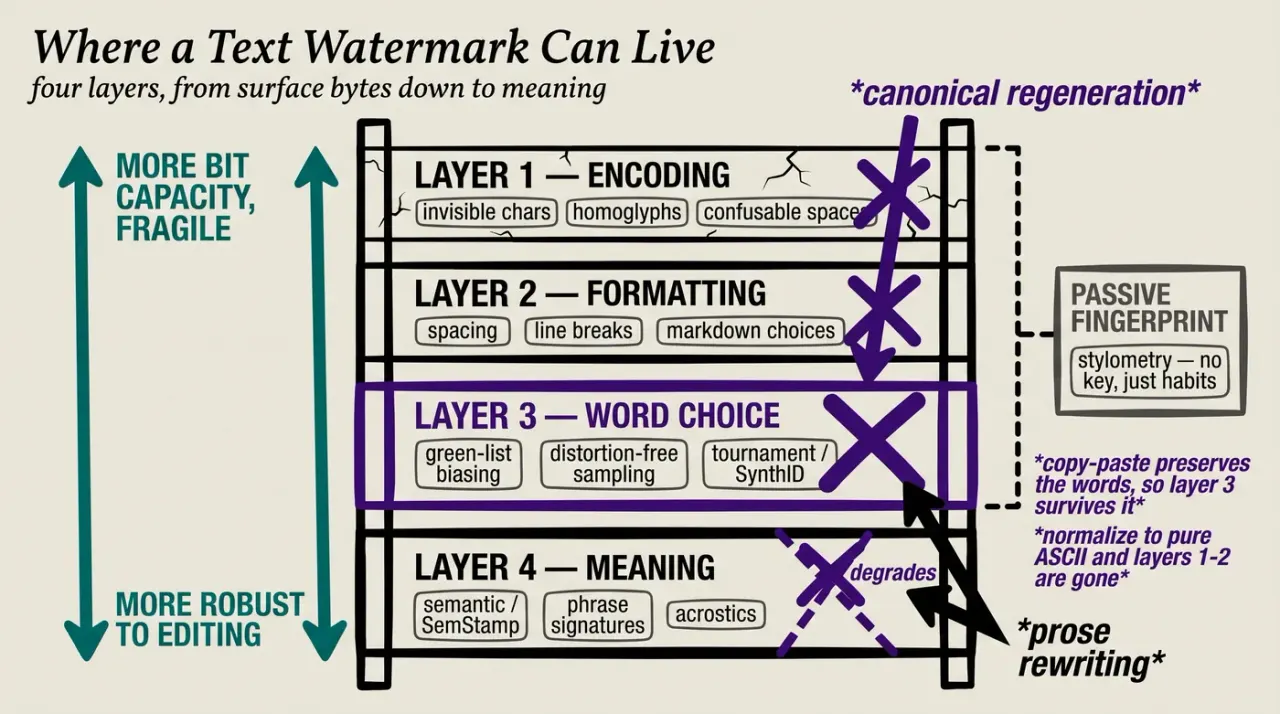
Diagram of the four layers a text watermark can live in, from encoding down to meaning, with the two bypasses canonical regeneration and prose rewriting crossing out the layers they strip/images/where-watermarks-hide-in-text-layers.webp/images/where-watermarks-hide-in-text-layers.webp On August…
A shift from a focus on latency to building better AI models, owning the full stack from applications to building custom hardware, very different incentives to most tech companies in play, and more
The Apache Trusted Releases (ATR) platform, a new tool from the ASF Tooling Initiative, is making it easier for open source maintainers across hundreds of independently governed ASF projects to ship secure, compliant releases without adding to their workload. ATR automates the parts of the release…
Posted by Toni Heidenreich, Software Engineer, Android Media3 1.11 is out. Powering the vast majority of top Android media apps, this release brings new features, bug fixes, and improvements across playback, editing, and UI components. We're expanding our Jetpack Compose UI modules with…
Radiology AI is evolving beyond report generation. CARE-X explores a unified approach that combines flexible reasoning, calibrated predictions, and measurement-based tools for chest X-ray interpretation. The post Introducing CARE-X: Towards Clinically Useful Radiology VLMs with Auxiliary…
Charcoal sketch of a colossal kneeling figure made of hundreds of interlocking hands, reaching down with open palms toward a vast crowd of suffering people/images/nobody-asked-for-ai-header.webp/images/nobody-asked-for-ai-header.webp With lots of competition, the argument that "nobody asked for…
Long-running AI agents spend most of their time on high-volume execution: tool calls, result validation, and subagent delegation. Using a frontier reasoning...
Building an AI agent does not end with choosing a single model. Each model has its own strengths, weaknesses, and cost profile, which can shift from one...
Today Databricks announced that Electric, the team behind PGlite and the Electric sync engine, is joining Databricks. We have our own reason to celebrate: Electric is joining the Neon team within Databricks, bringing lightweight WASM Postgres + real-time sync to Neon.
We are rapidly approaching budget season and planning for contingencies in 2027. Perhaps open-weight models should be part of your fall planning. Last year, DeepSeek created a scare for the American AI industry when it created a model that cost a fraction to develop relative to its U.S…
Mistral is bringing together the inference infrastructure, open models, and long-term commitments Europe needs to control its AI future, and setting a roadmap for the world.
CISA has added three new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-20349 Cisco Secure Firewall Adaptive Security Appliance (ASA) and Firewall Threat Defense (FTD) Heap Inspection Vulnerability CVE-2026-68820 Microsoft…
When tasked with building a highly interactive, tactile web experience, the architecture must serve the art direction. In this article, Alexey Kopytin explains their architectural rationale for building a digital stress-relief squeeze toy game using Lottie animations, DOM events, and distance-based…
Ryan is joined by Coder’s Rob Whiteley to chat about why tokenmaxxing isn’t proving real value and just triggering Goodhart’s Law, how release speed and PR merges can help you measure agentic outcomes with or without a human-in-the-loop, and what the democratization of skills means for junior…
Over the past year, AI models have become much more capable of performing cybersecurity work. These changes are reshaping both the threats facing the web and the tools available to defend it. Right now, defenders have an advantage because they can use stronger models for defensive work than the…
This vulnerability allows remote attackers to execute arbitrary code on affected installations of OriginLab Origin Viewer. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8…
This vulnerability allows local attackers to escalate privileges on affected installations of Parallels RAS Client. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The…
This vulnerability allows local attackers to escalate privileges on affected installations of Parallels RAS Client. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The…
This vulnerability allows remote attackers to execute arbitrary code on affected installations of OriginLab OriginPro . User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The…
This vulnerability allows remote attackers to execute arbitrary code on affected installations of OriginLab OriginPro. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The…
This vulnerability allows remote attackers to execute arbitrary code on affected installations of OriginLab Origin Viewer. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8…
This vulnerability allows remote attackers to execute arbitrary code on affected installations of OriginLab OriginPro. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The…
AI Gateway Production Index — August 2026 AI Gateway May June July Every month,routes tens of trillions of tokens between production applications and AI labs. That traffic gives us a view of what AI usage actually looks like in today's enterprise, and we publish it here monthly. See the Production…
In an exchange filing, HCLTech said its initial investigation found the data "may be limited and dated to a few years back." The company said there was no evidence of a breach of its systems, and no indication that any client engagement was affected.
Imagine if McDonald’s could use trademark law to control how you use the term “fast food.” Or if the Canadian government could stop you from using the word “Canada” in the title of a book about the country and its people. That wouldn’t just be absurd; it would be an unacceptable obstacle to…
Running untrusted code safely requires more than separating it from the host. You also have to control what that code can reach. This matters more as AI agents gain the ability to read files, execute commands, install packages, and generate programs of their own. A microVM can prevent that code…
LaunchDarkly Vercel Marketplace is now available on the, allowing you to quickly get started with feature flags without additional setup. You can: vercel install launchdarkly @flags-sdk/launchdarkly Flags SDK To get started, run, add theadapter, and declare a flag with the: Using a coding agent?…
Subtransactions can slow down your entire PostgreSQL server and break your high availability strategy by keeping new read replicas from accepting connections.
bitdrift joins ClickHouse’s House Mates program with a mobile observability integration, bringing mobile-native telemetry, tracing, and debugging to ClickStack.
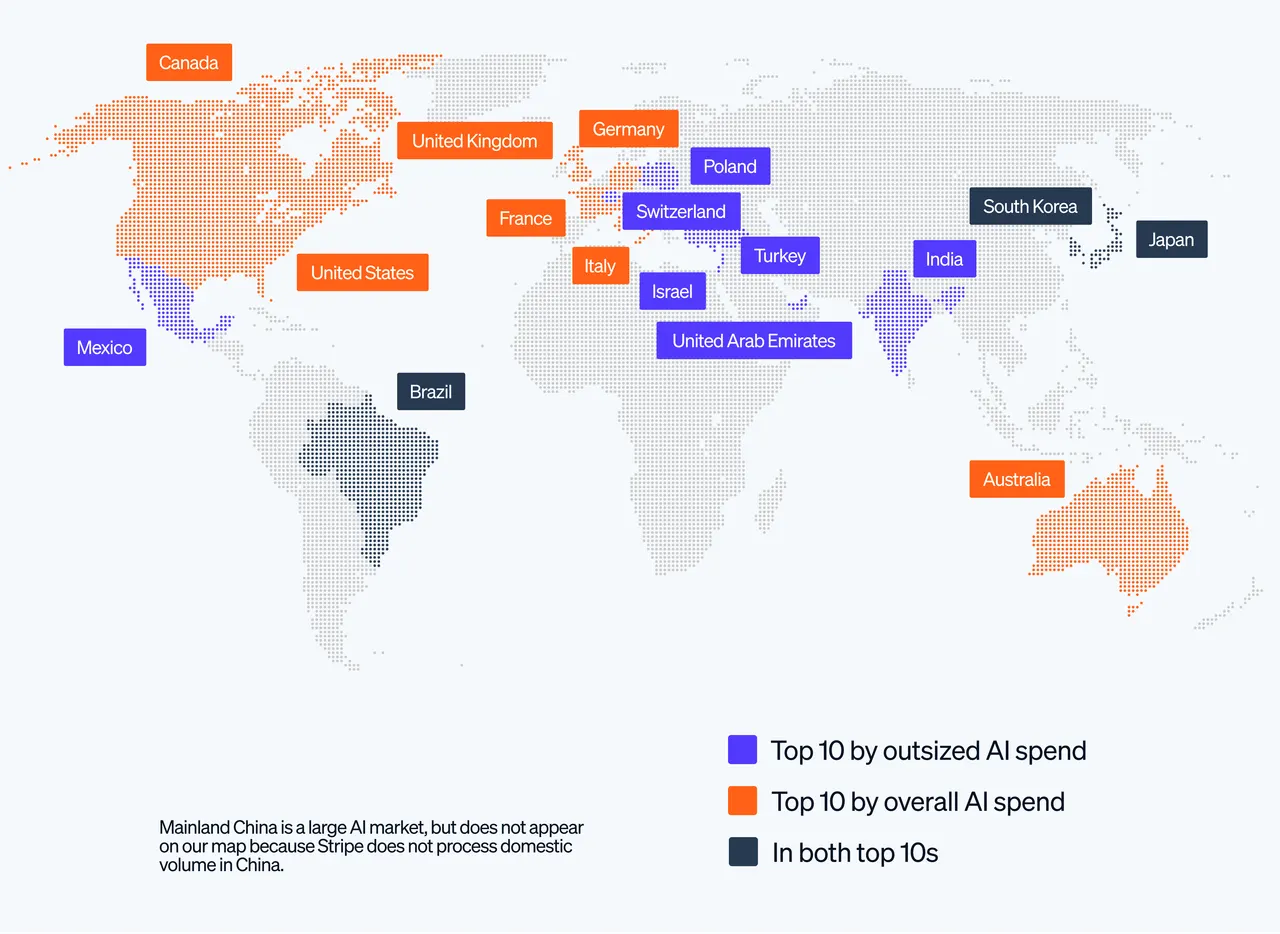
AI companies are undergoing rapid global expansion while achieving unprecedented rates of growth. We analyzed Stripe data to understand where global demand is the strongest, and how companies can build to best capture that demand.