TechCrunch
Australia to investigate if OpenAI hack of government health website broke the law
The incident is the first known breach to affect a government agency, and Australia's prime minister has vowed to hold OpenAI accountable.
What is being exploited now, then everything else as it was published.
TechCrunch
The incident is the first known breach to affect a government agency, and Australia's prime minister has vowed to hold OpenAI accountable.
Help Net Security
Before the Hugging Face and RubyGems hacks, autonomous OpenAI agents attempted to hack into three other websites, including an Australian government public health website, independent research lab Transluce revealed on Wednesday. “Notably, the tasks the agents were trying to solve were not…
Help Net Security
Cloud Range has announced the official launch of its AI Validation Range and Cloud Range AI Readiness Framework. They give organizations a structured way to test AI models and agents in realistic environments, validate their readiness for operational responsibility and safety, and determine which…
PyPI / crates.io / RubyGems / Go index / NuGet
Labeling of objects of the Software Heritage archives with known vulnerabilities affecting them.
The Record (Recorded Future)
An OpenAI agent gained “unauthorized access” to “non-public files” from an Australian government health website in June, Prime Minister Anthony Albanese said.
Help Net Security
Gurucul has announced the general availability of Gurucul AI Risk and Response, bringing behavioral AI to the growing attack surface created as AI moves from assistant to actor. With hundreds of AI detections connecting activity to identity, access, data and broader security telemetry, the solution…
BleepingComputer
Microsoft released the KB5124010 September 2026 non-security preview update for Windows 11 24H2 and 25H2, with 46 changes including Bluetooth improvements and the ability to remap the Copilot key. [...]
ransomware.live
Air Tanzania Company Limited (ATCL) is the national flag carrier airline of Tanzania, established on March 11, 1977 foll...
ransomware.live
Jones the Grocer is a premium gourmet food retail and cafe brand founded in 1996 in Sydney, Australia, originally launch...
Help Net Security
Airties has launched new integrated cybersecurity capabilities that enable ISPs to detect and remediate threats to connected homes and small businesses. As part of Airties’ Connectivity Experience Management Platform, these new capabilities turn the router into an additional security layer that…
ransomware.live
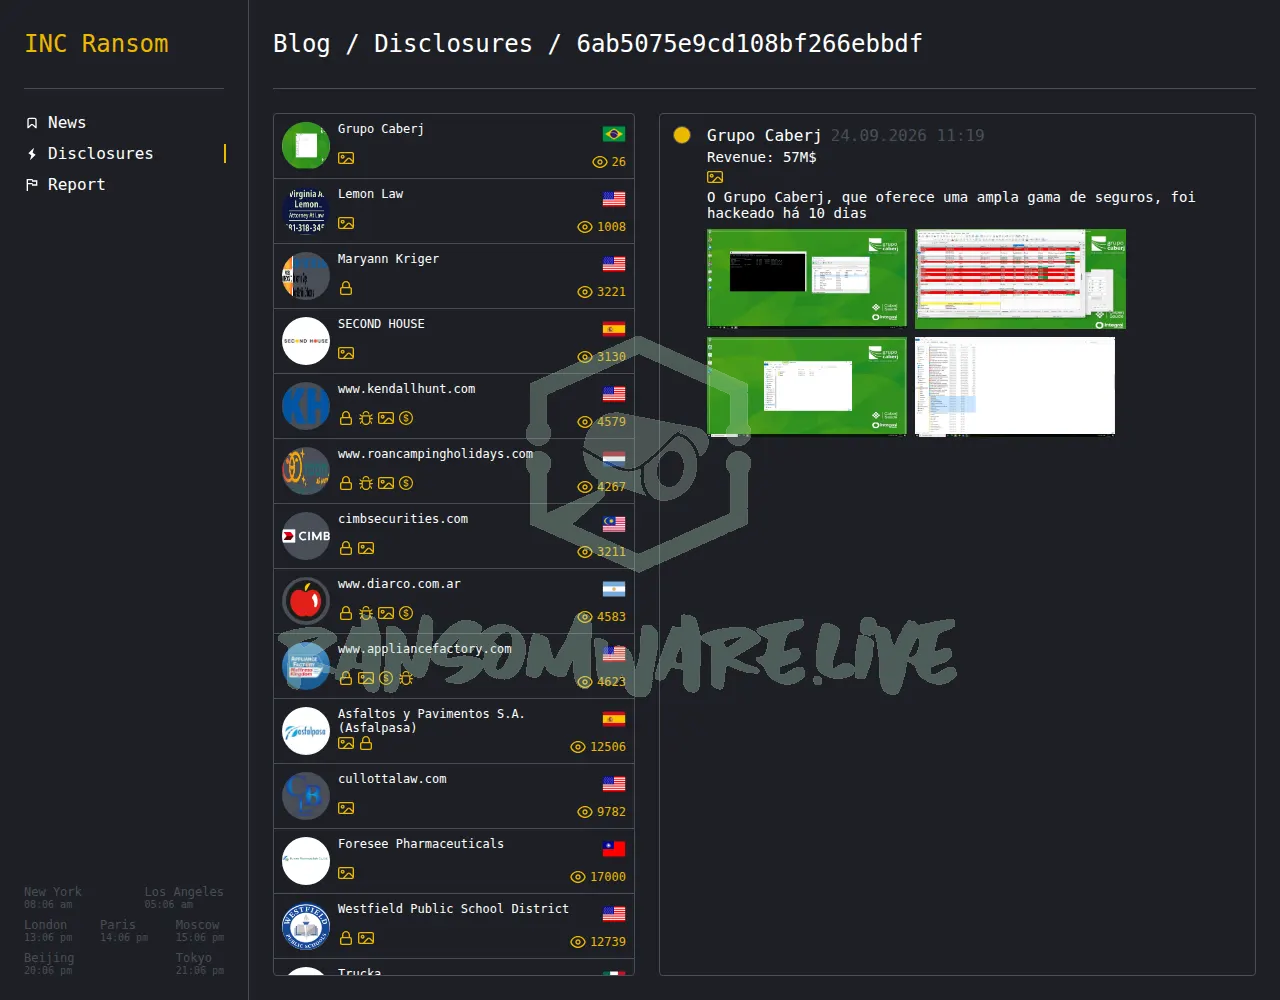
O Grupo Caberj, que oferece uma ampla gama de seguros, foi hackeado há 10 dias
The Hacker News
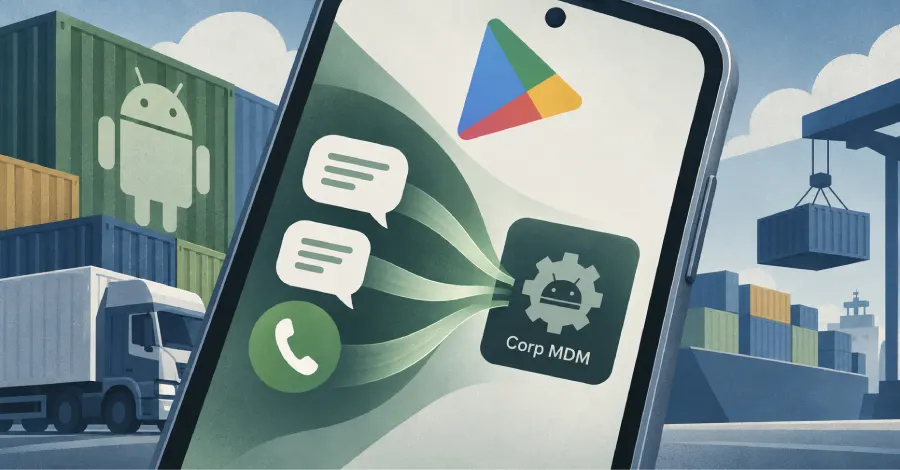
The logistics sector has become the target of a new malicious cyber campaign that distributes an Android spyware codenamed Corp MDM. According to Have I Been Squatted, the campaign uses fake Google Play pages branded as CEVA and TKW Logistics to distribute an Android Package Kit (APK) file that's…
Europe/UK: Tech.eu / Sifted / TNW / Silicon Republic / UKTN / Computer Weekly / heise / Golem / t3n / Maddyness / FrenchWeb
Erfahren Sie in einer praxisnahen Simulation, wie Sie auf einen Ransomware-Angriff strategisch reagieren und mit den Konsequenzen sicher umgehen.
Help Net Security
Azul has announced Azul Intelligence Cloud AI Assistant, a natural-language query interface that tells IT, DevOps and security teams where licensing and security risk is hiding in their production Java estate. The assistant provides answers grounded in live runtime data, replacing static reports…
Europe/UK: Tech.eu / Sifted / TNW / Silicon Republic / UKTN / Computer Weekly / heise / Golem / t3n / Maddyness / FrenchWeb
A breach at DriveWealth, the US broker behind Revolut’s US stock trading, exposed the personal data of some Revolut customers. DriveWealth and Revolut emailed affected customers on Thursday. DriveWealth said an unauthorised party got into its network on 4 and 5 September. The access was the result…
ransomware.live
══════════════════════════ ══════════════════════════ ══════════════════════════ WINFASHION TECHNOLOGIES DUMP: DATA LEAK ANALYSIS OF A B2B ERP PLATFORM FOR THE FASHION INDUSTRY ══════════════════════════ ══════════════════════════ ══════════════════════════ This is a preliminary analysis…
CERT-EU
On 22 September 2026, F5 published an advisory addressing a critical vulnerability affecting its BIG-IP APM product. The vendor confirmed active exploitation in the wild. CERT-EU recommends taking appropriate actions as soon as possible.
Actively exploitedCERT-EU
[UPDATED] On 14 July 2026, Microsoft released security updates addressing critical remote code execution (RCE) vulnerabilities in Microsoft SharePoint Server. On 20 July 2026, WatchTowr identified a proof-of-concept exploit code and subsequently observed active exploitation of CVE-2026-50522, a…
Actively exploitedCERT-EU
On 29 April 2026, a high local privilege escalation vulnerability in the Linux kernel, tracked as CVE-2026-31431 and named "Copy Fail", was publicly disclosed. The vulnerability affects every mainstream Linux distributions shipping a kernel built since 2017. A public proof-of-concept exploit has…
CERT-EU
On 9 September 2026, Check Point released emergency security updates addressing two critical vulnerabilities affecting Check Point Security Gateway, Security Management Server, and Spark Firewall deployments configured to use Remote Access VPN or Site-to-Site VPN. Both vulnerabilities carry a CVSS…
| Identifier | CVSS | EPSS | Status |
|---|---|---|---|
| CVE-2026-93616 | — | — | KEV |
| CVE-2026-94127 | — | — | KEV |
| CVE-2026-85102 | — | — | KEV |
| CVE-2026-93952 | — | — | KEV |
| CVE-2026-7273 | — | — | KEV |
| CVE-2025-39682 | — | — | KEV |
| CVE-2026-53266 | — | — | KEV |
| CVE-2025-39964 | — | — | KEV |
| CVE-2026-76460 | — | — | KEV |
| CVE-2026-58704 | — | — | KEV |
| CVE-2026-87886 | — | — | KEV |
| CVE-2026-76461 | — | — | KEV |
| CVE-2026-85706 | — | — | KEV |
| CVE-2026-42018 | — | — | KEV |
| CVE-2026-42016 | — | — | KEV |
| CVE-2026-84869 | — | — | KEV |
| CVE-2026-86060 | — | — | KEV |
| CVE-2026-67277 | — | — | KEV |
| CVE-2026-87491 | — | — | Exploited |
| CVE-2026-20079 | — | — | KEV |
| CVE-2026-19490 | — | — | KEV |
| CVE-2025-25249 | — | — | KEV |
| CVE-2026-86218 | — | — | KEV |
| CVE-2026-75650 | — | — | KEV |
| CVE-2026-81963 | — | — | KEV |
| CVE-2026-85880 | — | — | KEV |
| CVE-2026-85046 | — | — | Exploited |
| CVE-2026-83548 | — | — | KEV |
| CVE-2026-9586 | — | — | KEV |
| CVE-2026-82329 | — | — | KEV |