CVE-2026-96951
Improper neutralization of special elements used in a command ('command injection') in Windows Shell allows an unauthorized attacker to bypass a security feature over a network.
- CVSS
- 8.8
- EPSS
- —
- CISA KEV
- Not listed
- Exploitation
- active
- Public exploits
- None seen
- State
- PUBLISHED
Coverage
Critical 60Tenable ResearchAuthoritative. Authoritative publisher: a primary source, or a newsroom with formal editorial standards
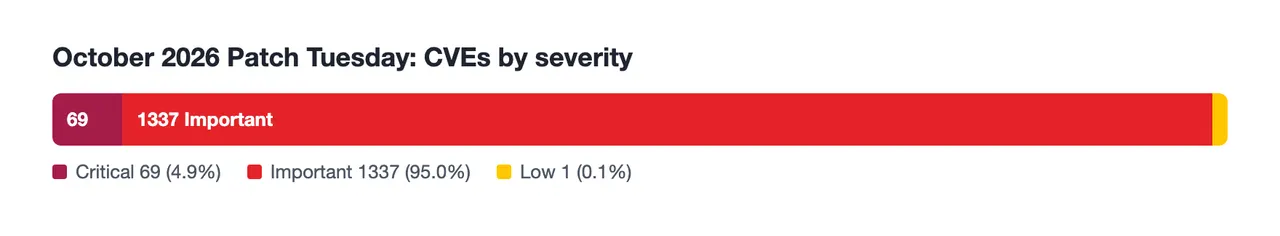
Microsoft’s October 2026 Patch Tuesday addresses 1407 CVEs (CVE-2026-96951)
69Critical 1337Important 0Moderate 1Low Microsoft addresses 1407 CVEs in the tenth Patch Tuesday of 2026, marking the second consecutive month to reset the bar as the largest Patch Tuesday release. This month’s updates include patches for two zero days, including one that was exploited in the wild…
Actively exploitedCritical 100CISA advisories & alertsAuthoritative. Authoritative publisher: a primary source, or a newsroom with formal editorial standards
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-96951 Microsoft Windows Command Injection Vulnerability CVE-2026-104935 Ivanti Connect Secure Authentication Bypass by Spoofing Vulnerability These types…
What we observed
No signals recorded