CVE-2026-111497
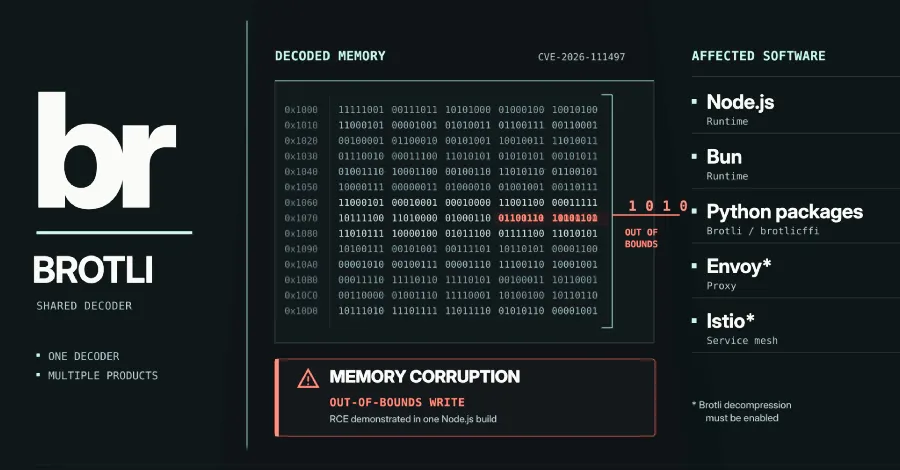
A buffer overflow vulnerability in the Brotli decoder (c/dec/decode.c) in Google Brotli versions 1.0.3 through 1.2.0 on all platforms allows a remote unauthenticated attacker to corrupt adjacent decoder state memory, disclose sensitive memory contents, cause a denial of service, or potentially execute arbitrary code using a crafted Brotli-compressed stream. Users need to update any Brotli libraries or binaries between 1.0.3 through 1.2.0 to the latest available version: 1.0.10 or 1.1.1 or 1.2.1.
- CVSS
- 9.2
- EPSS
- 0.005 (40.5th percentile)
- CISA KEV
- Not listed
- Exploitation
- none
- Public exploits
- None seen
- State
- PUBLISHED
Coverage
The Hacker NewsSpecialist. Specialist publisher: established trade press, or expert analysis with a track record
Brotli Decoder Flaw Behind Node.js RCE Also Affects Bun, Python and Other Widely Used Software
A memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli. Tracked as CVE-2026-111497, the flaw allows crafted compressed data to overwrite…
What we observed
- osv ecosystemosv
- osv ecosystemosv
- osv ecosystemosv
- osv ecosystemosv