CVE-2015-3306
The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the site cpfr and site cpto commands.
- CVSS
- —
- EPSS
- 0.968 (99.9th percentile)
- CISA KEV
- Added 2026-10-08, due 2026-10-11
- Exploitation
- active
- Public exploits
- 18 repositories
- State
- PUBLISHED
Coverage
Actively exploitedCritical 100The Hacker NewsSpecialist. Specialist publisher: established trade press, or expert analysis with a track record
Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies
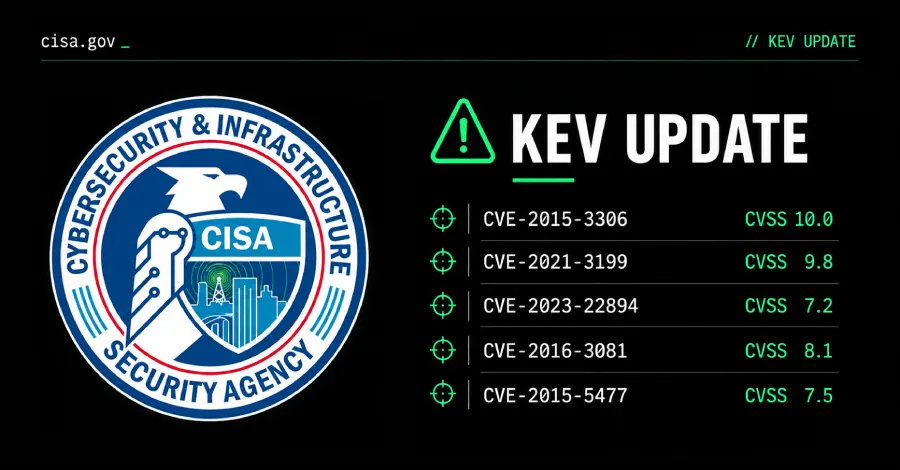
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in question are listed below - CVE-2015-3306…
What we observed
- poc publishedpoc-in-github
- kev addedcisa-kev